In today’s digital age, the General Data Protection Regulation (GDPR) has become a cornerstone for data privacy in the European Union. For businesses, this means adhering to strict guidelines on how personal data is handled, stored, and ultimately destroyed. Document destruction is a critical aspect of GDPR compliance, ensuring that sensitive information does not fall into the wrong hands. This guide provides a practical overview of what must be shredded by law to maintain compliance and protect your business from potential fines.
What Documents Must Be Shredded Under GDPR?
Under GDPR, certain types of documents containing personal data must be securely destroyed once they are no longer needed. Shredding compliance essentials is a recommended method to ensure that the information cannot be reconstructed. This not only helps in maintaining compliance but also safeguards your business from data breaches.
Documents Requiring Shredding Under GDPR
- Employee records containing personal data
- Client contracts and agreements
- Financial statements and reports
- Medical and health records
- Marketing lists with personal information
- Supplier and vendor agreements
- Confidential internal communications
Understanding GDPR’s Impact on Document Destruction
GDPR has redefined how businesses handle personal data, emphasizing the need for secure destruction methods. The regulation mandates that organizations must not only collect and process data lawfully but also dispose of it responsibly when it is no longer necessary. This is where shredding comes in as a secure method to prevent unauthorized access to sensitive information.
Failure to comply with GDPR’s data destruction requirements can result in significant fines and reputational damage. Therefore, businesses must establish a robust document management policy that includes regular audits and employee training on proper document disposal practices. By doing so, companies can ensure that they are not only compliant but also protecting their clients’ and employees’ privacy.


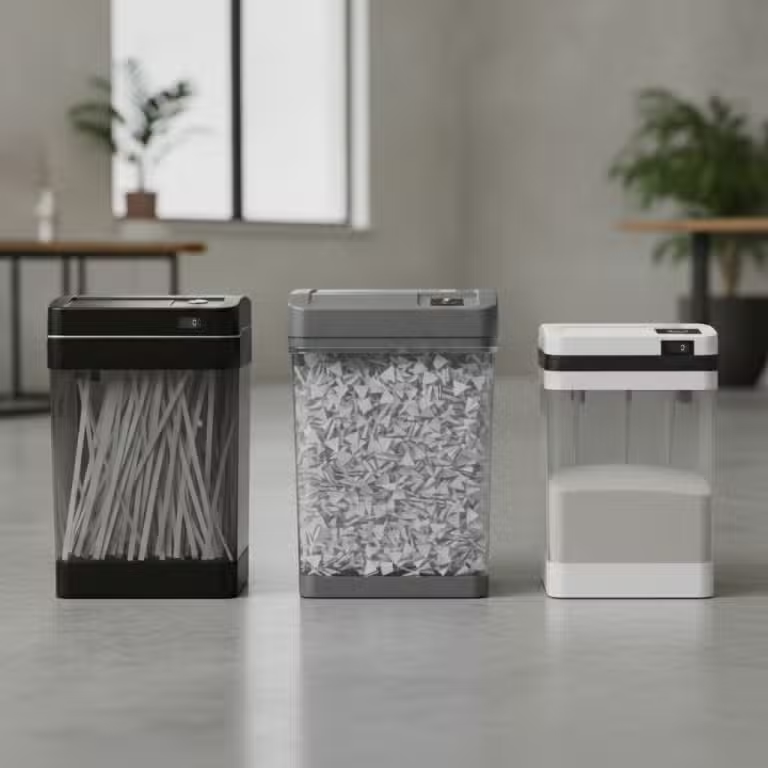
Viking Shredder 18 Sheets Cross Cut Security Level P-4 28 L OS1801CI

Viking Shredder 12 Sheets Cross Cut Security Level P-3 25 L OS1201D

Viking Auto Feed Shredder 120 Sheets Micro Cut Security Level P-4 23 L C233-B

Viking Shredder 10 Sheets Cross Cut Security Level P-4 10 L OS1006C

Viking Shredder 9 Sheets Micro Cut Security Level P-5 20 L OS901Mi
Best Practices for GDPR-Compliant Document Shredding
Implementing best practices for document shredding involves more than just purchasing a shredder. Businesses should categorize documents based on sensitivity and retention requirements, ensuring that only authorized personnel have access to sensitive information. Regularly scheduled shredding sessions can help maintain compliance and reduce the risk of data breaches.
Furthermore, it is advisable to work with certified shredding services that provide proof of destruction. This not only adds an extra layer of security but also offers documentation to demonstrate compliance during audits. By integrating these practices into your document management strategy, you can effectively mitigate risks associated with data breaches and non-compliance.
Document Retention and Shredding Requirements
| Document Type | Retention Period | Shredding Requirement |
|---|---|---|
| Employee Records | 5 years post-employment | Shred immediately after retention period |
| Client Contracts | 6 years after termination | Shred after retention period |
| Financial Statements | 7 years | Shred after retention period |
| Medical Records | 10 years | Shred once no longer needed |
| Marketing Lists | Until consent is withdrawn | Shred upon withdrawal of consent |
Ensuring GDPR Compliance Through Secure Document Destruction
In conclusion, GDPR compliance is not just about protecting data but also about demonstrating a commitment to privacy and security. By understanding the legal requirements for document destruction and implementing best practices, businesses can safeguard themselves against potential fines and enhance their reputation.
Remember, secure document destruction is a critical component of your overall data protection strategy. Stay informed, stay compliant, and protect your business and its stakeholders by adhering to GDPR’s document shredding requirements.
Frequently Asked Questions on GDPR and Document Destruction
What is GDPR’s stance on document destruction?
GDPR requires that personal data be securely destroyed when it is no longer necessary for the purposes for which it was collected. This includes physical documents, which should be shredded to prevent unauthorized access. The regulation emphasizes accountability and security, making document destruction a key aspect of compliance.
How can I ensure my business is compliant with GDPR shredding requirements?
To ensure compliance, implement a document management policy that includes categorizing documents based on their sensitivity and retention requirements. Schedule regular shredding sessions and consider using certified shredding services that provide proof of destruction. Training employees on proper document disposal practices is also crucial for maintaining compliance.
Are there specific documents that must be shredded under GDPR?
Yes, documents containing personal data such as employee records, client contracts, financial statements, medical records, and marketing lists should be shredded once they are no longer needed. The key is to ensure that these documents are disposed of in a manner that prevents unauthorized access.
What are the consequences of non-compliance with GDPR’s document destruction requirements?
Non-compliance with GDPR can result in substantial fines, which can be up to 4% of a company’s annual global turnover or €20 million, whichever is higher. Additionally, businesses may suffer reputational damage and loss of trust from clients and stakeholders, which can have long-term impacts.
Can I use a regular office shredder for GDPR compliance?
While a regular office shredder can be used, it may not provide the level of security required for highly sensitive documents. It’s advisable to use cross-cut or micro-cut shredders for better security. Alternatively, partnering with a certified shredding service can ensure that documents are destroyed in compliance with GDPR standards.